THE 2027 READINESS BRIFEING
What Insurance, Technology, and Legal Experts Want Leadership Teams to Know Before Planning BeginsJOIN US FOR OUR WEBINAR ON TUESDAY, SEPTEMBER 22ND at NOON
2027 planning is already underway. Budgets are being set. Priorities are being weighed. Technology investments are being evaluated. But most leadership teams are building next year’s plans while risk, regulation, cybersecurity, AI, insurance requirements, and legal exposure keep shifting around them.
Before you lock in your plans, there are questions worth asking now.
Join Drew Morrisroe, Spencer Pollock, and Alexandria Bretschneider for a 30-minute executive roundtable on what leadership teams should be addressing now, from three perspectives: technology, legal, and insurance.
This is not a trends presentation. It is a practical conversation about the issues you may be underestimating, the decisions that could create unexpected exposure in 2027, and the areas that deserve a place in your planning conversation before budgets and priorities are finalized.
THE CONVERSATION
The panel will address:
- What emerging risks are leadership teams still underestimating?
- How are AI, cybersecurity, data, and third-party relationships changing your exposure?
- What are insurers scrutinizing more closely?
- Where are companies creating legal risk faster than their policies and contracts can keep pace?
- Which technology investments are becoming business-critical rather than simply IT decisions?
- Where do legal, insurance, and technology responsibilities overlap, or fall between the cracks?
- What should your CEO, CFO, and COO address before finalizing 2027 plans?
Three Perspectives. One Conversation.
Insurance
- Are you protected?
- How are coverage requirements, exclusions, cyber risk, and underwriting expectations affecting your planning?
Technology
- Are you prepared?
- Is your organization ready for the technology, cybersecurity, data, and AI demands 2027 will bring?
Legal
- Are you defensible?
- Do your contracts, policies, governance, and internal practices reflect how your organization actually operates today?

Who Should Attend
CEOs, CFOs, COOs, business owners, board members, and other senior leaders involved in strategic planning, budgeting, risk management, and organizational decision-making.
The Goal
By the end of the conversation, you should leave with a clearer view of the questions to bring into your own 2027 planning discussions.
Before your plan is finalized, your leadership team should be able to answer three questions:
- Are we protected?
- Are we prepared?
- Are we defensible?
Your Guides During the 30 Minute Session
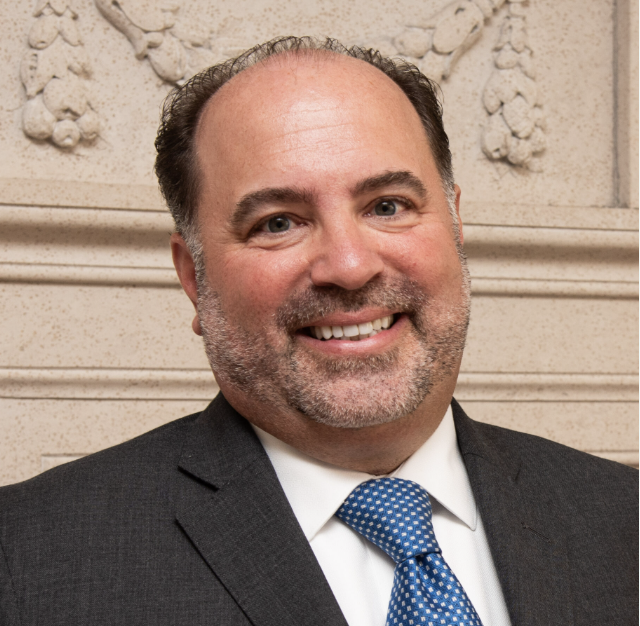
Drew Morrisroe
Founder & CEO, CTN Solutions
Strategic Leadership & Governance
Drew guides executive teams through governance, compliance, and strategic risk decisions. He helps boards and leadership translate cyber risk into business risk and build accountability frameworks that hold up under scrutiny.
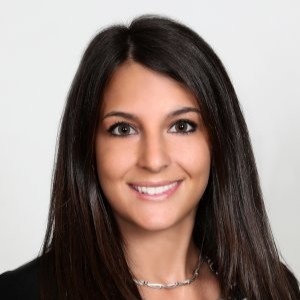
Alexandra Bretschneider
Vice President & Cyber Practice Leader at Johnson, Kendall & Johnson
Cyber Insurance & Legal Exposure
Alexandra advises executives on cyber insurance coverage and requirements, privacy litigation risk, and board-level accountability. She’s seen what happens when leadership assumes compliance equals security and helps organizations close the gap before incidents occur.
Spencer Pollock
Data Privacy and Cybersecurity Attorney, McDonald Hopkins
Security Operations & Incident Response
Spencer leads security operations and incident response for organizations under attack. He’s worked inside breaches where executives thought they were protected and helps leadership understand what attackers exploit and how to detect threats faster.